PHP Hacking Attempts Hit Millions in Hours, Recovery Takes Days
Exploit attempts against PHP’s flaws leapt from thousands to millions within hours, yet Finland’s state IT provider warns reopening shuttered services can take days or even weeks.

Cloudflare reported millions of attempts to exploit two critical PHP flaws on Thursday, October 22, a day after the PHP project shipped emergency fixes for the vulnerabilities.
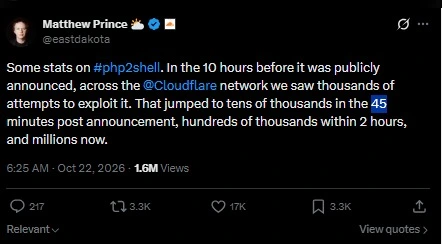
Chief executive Matthew Prince said on X that traffic against its network climbed from thousands of attempts before the disclosure to millions within hours.
Governments and companies worldwide took services offline as a precaution, Reuters reported, as PHP reportedly underpins roughly 70% of websites.
The surge matters because attackers moved far faster than administrators can patch and test.
How Cloudflare Watched PHP Exploit Attempts Reach Millions
In the ten hours before PHP’s announcement, Cloudflare’s network logged thousands of attempts. Within 45 minutes of it, Prince noted the count was tens of thousands, then hundreds of thousands inside two hours, and millions after that.
Those numbers describe attempts, not confirmed break-ins.
The speed fits a warning from Madeline Lawrence, co-founder of Belgian firm Aikido Security, who told Reuters that details of the flaws became public before fixes were ready and that attackers can now use AI to exploit them, a method not new.
Reuters also reported that the flaws had sat in PHP for years until AI tools uncovered them. So the same technology now sits on both sides of the race.
Why Governments From Finland to the UK Pulled Websites Offline
Reuters described emergency shutdowns of banking, airline, rail, tax and government services across the globe.
Finland’s state IT provider Valtori blocked public web services and patched overnight, though director general Hannu Naumanen warned that rigorous testing means restoration “can take days or even weeks.”
Tencent Cloud, one of China’s largest providers, urged customers to install updated PHP versions without calling for widespread shutdowns, and several Asian governments ordered cybersecurity inspections.
In Britain, Baroness Lloyd of Effra told the House of Lords that 32 UK government services were unavailable and four partly so, The Independent reports.
The Office for Budget Responsibility and the Oxfordshire and Hillingdon councils were reportedly among those forced to update.
Why PHP Owners on Older Versions Face the Longest Exposure
Every active PHP installation is vulnerable, with mod_php setups reportedly facing extreme risk because unauthenticated requests can fire before application code runs.
Older software bears the heaviest burden. Official fixes covered only supported branches, while legacy versions received nothing more than manual source backports.
Security firms reportedly estimate that 59% of 2.24 million internet-facing PHP hosts run on versions with no patch coming.
Compounding the crisis, a 2024 audit had already spotted early signs of the flaw, but resource shortages at the PHP Foundation stalled the fix. This left defenders trailing long before the leak ever occurred.
Source: Millions of hacking attempts as companies, governments rush to patch PHP flaws